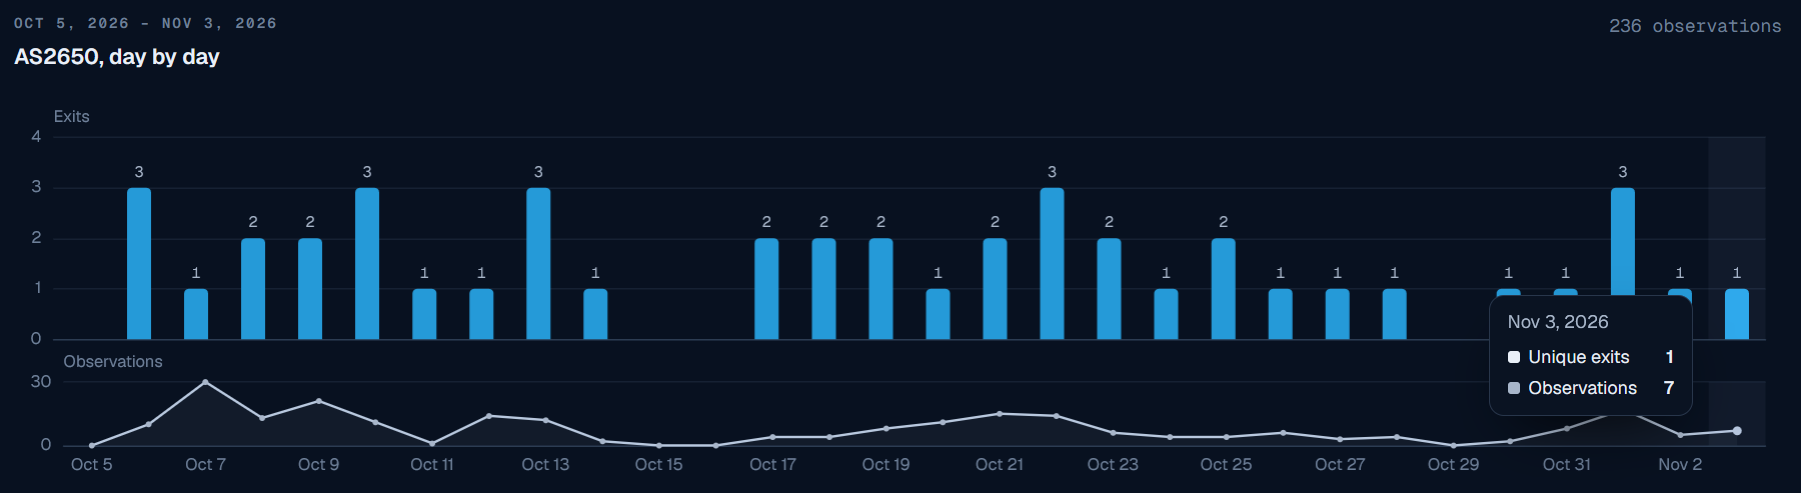
Our new Residential Proxy Observatory shows residential proxy traffic exiting the White House network: 236 times in 30 days, through 28 public proxy services.
A botnet implies a level of control over the compromised device, normally achieved through exploits. A residential proxy is done through taking advantage of technically naive users, rather than exploits (proxyware, sort of like spyware/adaware) and doesn’t aim to give control over the target device just over their internet connection. Botnets are run by individuals/hacking groups, and residential proxies are provided by “legitimate” businesses. In theory, they can both be used for the same purpose of DDOSing a target, but as most residential proxy resellers try and position themselves as legitimate, they are less likely to support a client that is using their service to DDOS people
‘Control over the device’ in botnets is practically also just the network. Bots are also created due to users being naive, like positioning iot devices open to the internet, running insecure stuff etc
The exploit route for RPs is also malicious, social engineering. Get stuff for free. Nobody is actually aware of what they are doing here.
I agree on the superficial legality. Like a share hoster deleting links in stead of content etc.

A botnet implies a level of control over the compromised device, normally achieved through exploits. A residential proxy is done through taking advantage of technically naive users, rather than exploits (proxyware, sort of like spyware/adaware) and doesn’t aim to give control over the target device just over their internet connection. Botnets are run by individuals/hacking groups, and residential proxies are provided by “legitimate” businesses. In theory, they can both be used for the same purpose of DDOSing a target, but as most residential proxy resellers try and position themselves as legitimate, they are less likely to support a client that is using their service to DDOS people
‘Control over the device’ in botnets is practically also just the network. Bots are also created due to users being naive, like positioning iot devices open to the internet, running insecure stuff etc The exploit route for RPs is also malicious, social engineering. Get stuff for free. Nobody is actually aware of what they are doing here.
I agree on the superficial legality. Like a share hoster deleting links in stead of content etc.